Security that holds up under pressure.
Vulnerability assessment, firewall and WAF rules, malware removal, SSL/TLS configuration and a recovery plan that has actually been tested.
Most website compromises are not targeted. They are automated scans finding an outdated plugin, a weak admin password or a forgotten staging site left open to the internet.
We close those doors, then watch the ones that are left.
Tell us about your site
Thanks, .
Your details are captured in this preview. Connect this form to your CRM or email endpoint before launch so requests reach the team.
Close the gaps, then keep watching
Security work splits into two halves that both matter. The first is the audit and the fixes: what is out of date, what is exposed, what permissions are wider than they need to be, which certificates are misconfigured.
The second is everything that happens afterwards — patch discipline, malware scanning, file integrity monitoring and alerting, because a site that was secure in March is not necessarily secure in September.
And because no defence is perfect, the work includes a recovery plan with backups that have been restored in a test, so a bad day is an inconvenience rather than a crisis.
What’s included
Fixed scope agreed in writing before we start, so you know exactly what is delivered and when. Anything outside it is quoted separately rather than absorbed quietly.
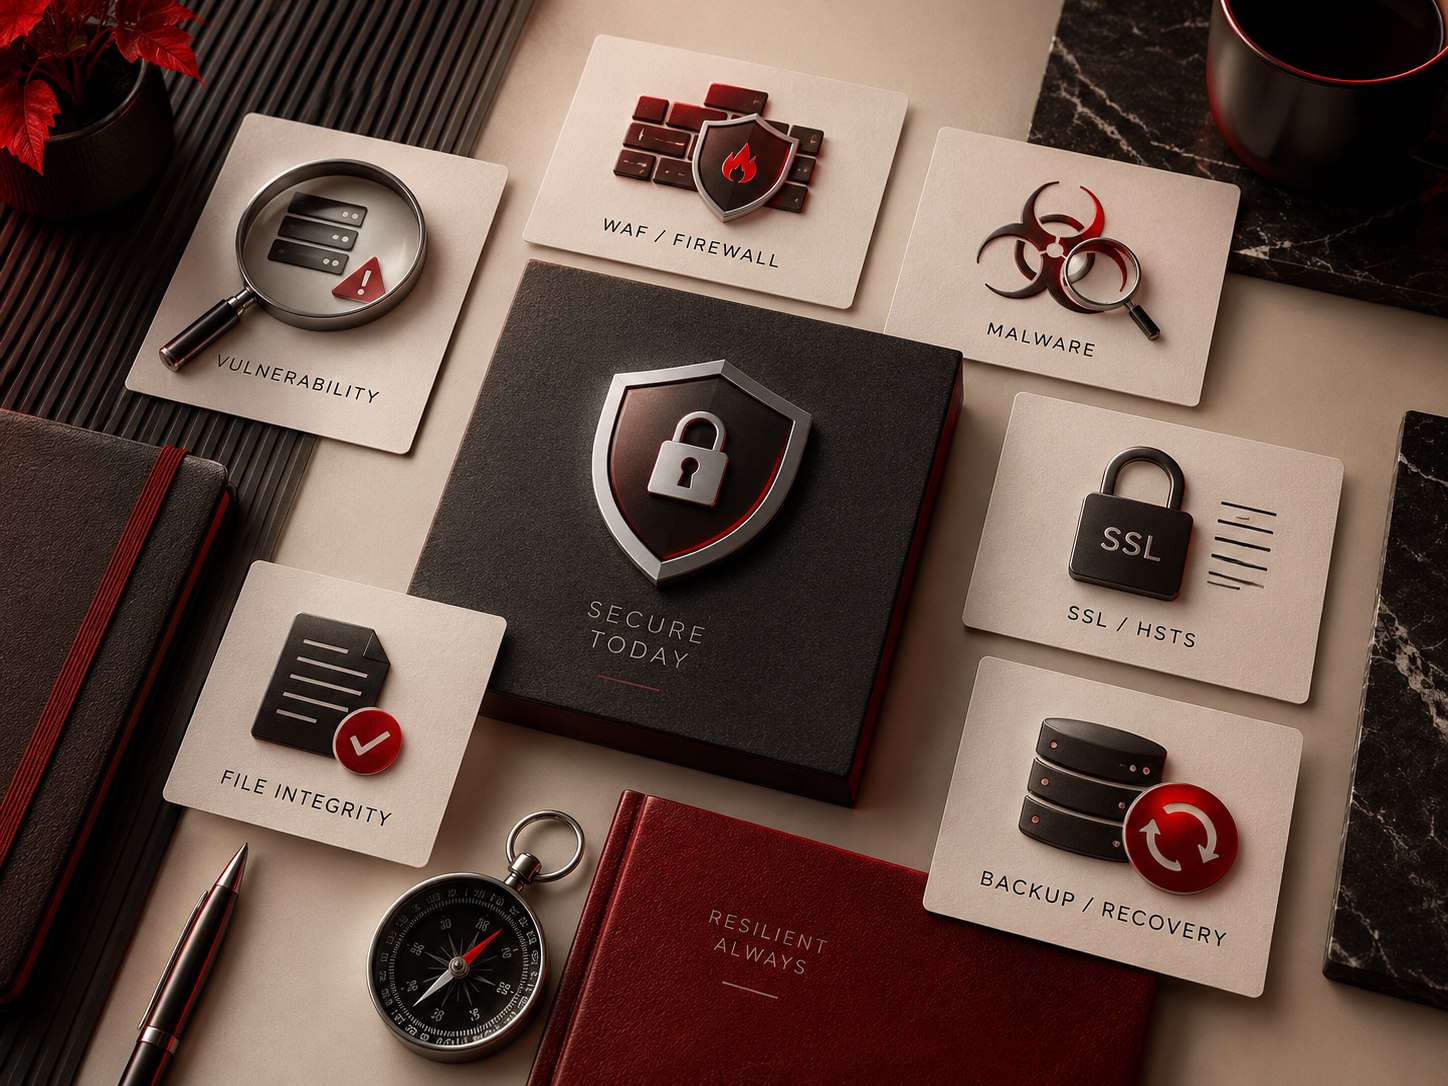
- Vulnerability assessment
- WAF and firewall configuration
- Malware scanning and removal
- SSL/TLS and HSTS setup
- File integrity monitoring
- Tested backup and recovery plan
Let’s close the gaps.
Tell us where things stand today and we’ll reply within one business day with an approach and a realistic estimate.
Why teams hand us the infrastructure
Hosting is usually someone's side job until the day it goes wrong. Here it is a dedicated team with a documented runbook, so there is no scramble when something breaks at 2am.
The people who manage your servers also built your website, which means no finger-pointing between a developer and a host when a page slows down.
You get root access and full ownership of everything, a monthly report of what changed, and a migration plan written down before anyone touches DNS.
Sized, migrated, maintained
We size the environment to real traffic, move you without downtime, then keep it patched and watched.
Plan
Traffic, storage and compliance needs mapped to the right environment.
Move
Staged migration with DNS cutover timed for zero downtime.
Optimise
Caching, CDN and database tuning so pages respond under load.
Support
Patching, backups, monitoring and a support line that answers.
Cyber Security Services questions
Scope, timelines, ownership and what we need from your side.
Yes. We isolate the site, remove the malware, patch the entry point and restore a clean backup, then monitor so the same route is not reused.
A domain-validated certificate covers most marketing sites. Organisation-validated or wildcard certificates make sense for stores, portals and multi-subdomain setups.
No. A properly configured firewall and CDN usually make a site faster, because malicious traffic is filtered before it reaches your server.
Yes. Monthly plans cover patching, malware scanning, integrity monitoring and a short report so you can see what changed.